Agentic pentesting
for software products
PenAgent's 42 agents attack your product the way hackers do. Regularly. The agent swarm makes continuous security possible.
523 findings across 22 projects · Built on 400+ penetration testing rounds
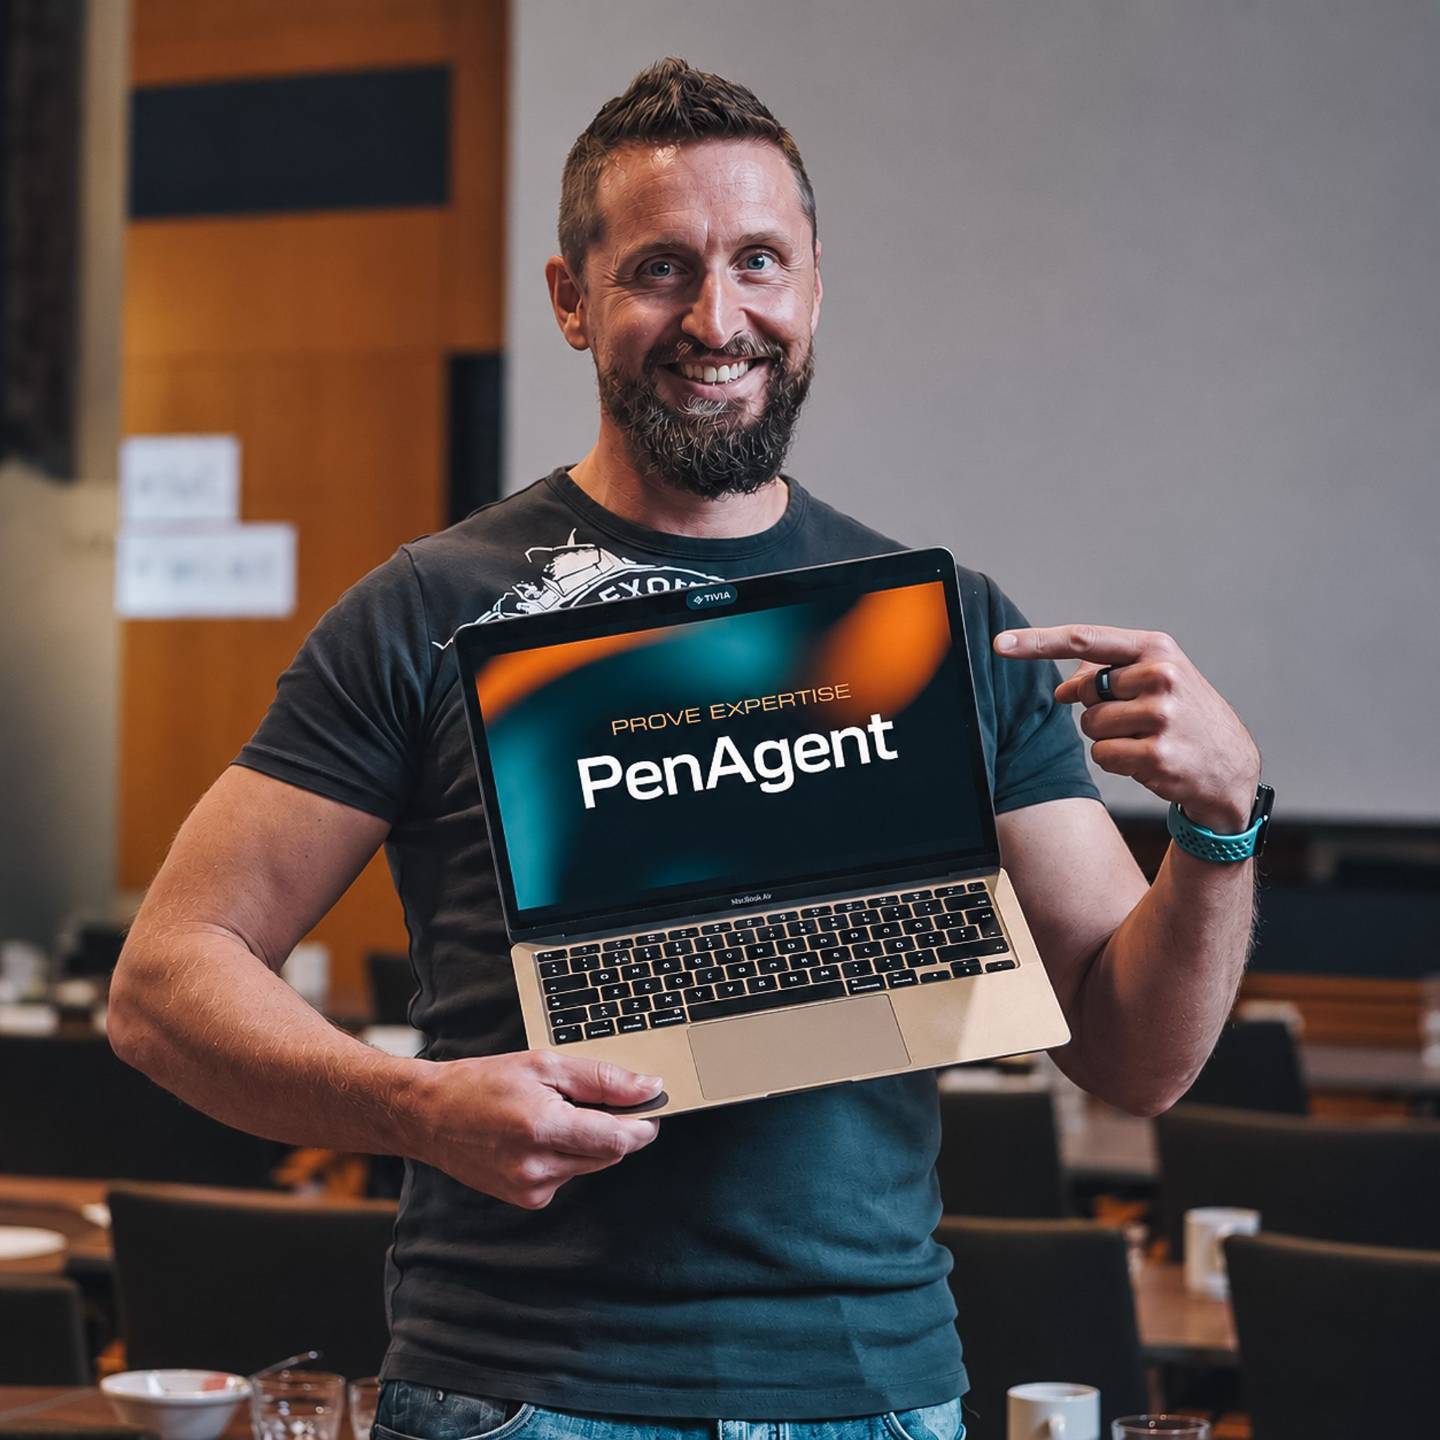
PROVE EXPERTISE · PenAgent™
PenAgent™ is built by Prove's pentesters, on the experience of more than 400 penetration testing rounds.
What has the agent swarm found?
We compared PenAgent™'s findings with expert-led penetration testing in five client projects. Over the same period, the agent swarm has been in use across 22 projects.
vulnerabilities that expert-led testing missed
of them was critical
of the same findings as the experts
findings reported in seven weeks
projects tested by the agent swarm
critical or high-severity findings (21%)
Comparison: five client projects in late summer 2026. Usage figures: findings reported by PenAgent between 18 Aug and 3 Oct 2026; merged and withdrawn findings are excluded. The results do not guarantee future findings.
What does a typical finding look like, how do severities break down, and why did experts miss some gaps? It's all in the PDF.
Download sample findings (PDF) →Why agentic pentesting?
Built by pentesters, run by agents
The experience of 400+ penetration testing rounds, encoded into 42 agents. A Prove pentester verifies every finding before it is reported.
Tell me more →Yes, when it actually attacks
A language model can describe an attack but can't execute it. PenAgent™'s specialist agents attack your running product and verify every finding.
See the comparison →Test every change, not just the release candidate
PenAgent™ tests each week's code in the same week, so there are no blind weeks between releases.
Why this matters →Time from vulnerability disclosure to exploitation has collapsed
– from years to hours.
The average time from discovering a vulnerability to exploiting it in real attacks has collapsed in the AI era.
A version released untested can be compromised over a single weekend.
Testing only the release is a thing of the past.
In security, reactive is too late.
Booking a penetration test for a release candidate is reactive by nature. Problems surface only once the version is already frozen. That was enough when exploiting a disclosed vulnerability took two years: a single snapshot gave a long safety margin.
In a ten-hour window there is no margin, and the gate still protects only one version. Proactive is the opposite: each week's code is tested in the same week, so the release candidate is already clean. And testing continues after the release too.
Test the release candidate
One intensive pentest round, then months of releases in the dark until the next round is booked.
The candidate is already clean
Each week's code is tested in the same week, so the round confirms rather than reveals.
The release candidate is the worst possible place to find an authentication bypass.
At that point the options are delaying the release or shipping with a known risk. Weekly testing moves the finding earlier, when fixing it is cheap — and turns the agent swarm from a booked inspection into an always-on safeguard.
The agent swarm, every week.
Run by our pentesters, every week
You keep the target ready
Make sure the test environment and test data are in place for each weekly run.
Our pentesters launch the run
A Prove pentester launches the agent swarm. No setup work on your side.
The agent swarm does the testing
PenAgent™ works through the target in parallel and verifies its findings.
Our pentesters review & deliver
A Prove pentester reviews the findings, removes the noise and delivers the report to your team.
Specialised agents – in use now, with more on the way.
Each agent is an expert in one attack area. 42 agents are now in production. They cover authentication, identity and access control most deeply, because that is where the most serious vulnerabilities hide. The agents also cover the full injection family, file uploads, AI features and the modern web surface.
Available today
42 production agentsCan an attacker log in as one of your users?
Every realistic route into an account that isn't theirs.
Can registration and password reset be abused?
The doors on both sides of the login screen.
Can login be brute-forced without anything stopping it?
Do automated attacks hit a wall, or keep going all night?
Can a user reach someone else's data or admin functions?
The rules on who can see and do what – OWASP's number one.
Can another site act through your logged-in users?
A user's own browser, borrowed by someone else's page.
Can malicious code run in your users' browsers?
Can a visitor's own session be turned against them?
Can your server be used to reach systems it shouldn't?
Your own backend as an attacker's proxy – or its file system.
Can your database be reached through a form field?
The oldest break-in method that still works. We prove it without reading or changing your business data.
Can your server be made to run something it shouldn't?
Input the server treats as commands rather than text.
Can file uploads be abused?
Accepting a file is a bug. Serving it back as code is a security incident.
Can your modern APIs be abused?
GraphQL and WebSockets follow different rules than your REST API.
Can your business rules be gamed?
Not a broken control, but a workflow used in an order nobody designed.
Can your AI features be turned against you?
If your assistant can call something, a chat message can try to reach it.
Is your infrastructure exposed or outdated?
The plumbing your application runs on.
Can the results be trusted and acted on?
A short, actionable list – not a wall of maybes.
"Why not just use a language model?"
"We already review our code with AI."
Both are reasonable – but neither is penetration testing. A single language model has no specialists, no memory and no evidence.
AI-assisted code review reads source code, but never attacks what you actually shipped. Only one of these three tells you what an attacker can reach in your running system.
General-purpose language model
"Why not just ask Claude or GPT to hack it?"
- ×One generalist does everything — shallow in every attack area.
- ×Loses earlier findings and context when the context window fills up.
- ×Works one step at a time — painfully slow on a large attack surface.
- ×Can describe an attack in detail, but has no tools to execute it.
- ×Reports plausible-sounding bugs it has never verified.
- ×No structure and no audit trail of what was actually tested.
AI-assisted code review
"We already review every PR with AI."
- ◐Reads source code — never attacks the system you actually shipped.
- ◐Can't see production configuration: TLS, exposed admin pages, outdated servers.
- ◐Blind to workflows that leave the codebase — such as SSO through an external provider.
- ◐Flags possible bugs without proof that they can be reached or exploited.
- ◐Reviewed code isn't the same as production — environment and configuration differences go unnoticed.
- ◐Can't confirm that a fix actually closed the gap after deployment.
PenAgent™ · agent swarm
Specialists that attack the running product.
- ✓42 specialists, each an expert in one attack area — and the number is growing.
- ✓Agents share what they learn during the engagement.
- ✓Agents work in parallel across hundreds of endpoints at once.
- ✓Tests the deployed system while logged in — the way an attacker actually meets it.
- ✓Every finding is verified before reporting.
- ✓Every run is logged and auditable.
Beyond the shallowness of scanners and the limits of manual penetration testing.
PenAgent™ reasons like a human tester, but starts in minutes and works at machine scale.
| ◇ PenAgent™ | Traditional scanner (DAST) | Manual penetration testing | |
|---|---|---|---|
| Availability | Every week — no waiting list | On demand | Booked months in advance |
| Verifies & exploits findings | Yes — verified, not guessed | No — signature-based guesses | Yes |
| Authentication & identity logic | Yes — dedicated agents | Largely blind | Yes |
| False-positive noise | Low — duplicates removed automatically | High | Low |
| Time to first result | Minutes to hours | Hours | Days to weeks |
| Cost of repeat runs | Fixed monthly price | Moderate | Hourly / daily rates |
PenAgent™ is now available. The agent swarm can start this week.
PenAgent™ is now available from Prove. The agent swarm starts on your target right away, even when our testers' calendars are full.
Want to hear more?
Proven methods, encoded into an agent swarm.
PenAgent™ is built by Prove's experienced penetration testing team — experts who have delivered more than 400 penetration testing rounds. Every agent encodes the craft, attack chains and judgement of those real engagements, so the swarm tests the way our experts do — not like a checklist.
Penetration testing rounds delivered for clients
Production agents in use now — and growing
A Prove pentester verifies every reported finding.
Our experts are booked months in advance.
Your testing doesn't have to wait.
Good pentesters are booked two to three months ahead. That is the honest reality of expert demand – and also two to three months of releases without oversight.
See what PenAgent has found.
Download the PDF: a sample finding from a real client project, the results of the comparison with expert-led testing, and the severity breakdown and weekly trend of 523 findings.
If you like, you can also book a 20-minute intro call with our expert on the thank-you page.
By submitting the form, you agree that we process your data in accordance with our privacy policy.
Download sample findings
We'll send the PDF to your email.
Practical questions, straight answers.
SECURITY AND DATA PROTECTION
What is our data used for?
Where is our data processed?
How are our credentials and findings protected?
THE SERVICE
What does PenAgent™ test?
How is the testing scope agreed?
How mature is the service?
EVIDENCE AND REPORTS
How does PenAgent™ compare with expert-led pentesting?
What do the reports contain?
CONTRACT
Which contract terms apply?
Prove Expertise Oy
Kirkkokatu 8A3, 90100 Oulu, Finland